The Lord of COBOL on Galactica Speaks: AI Is Scary, Please Don’t Fire the Security People
A witty take on AI security, trust, and risk—why giving autonomous systems access to code, money, and sensitive data should alarm everyone.
Exposing the limits, opportunities, and risks of AI
A witty take on AI security, trust, and risk—why giving autonomous systems access to code, money, and sensitive data should alarm everyone.
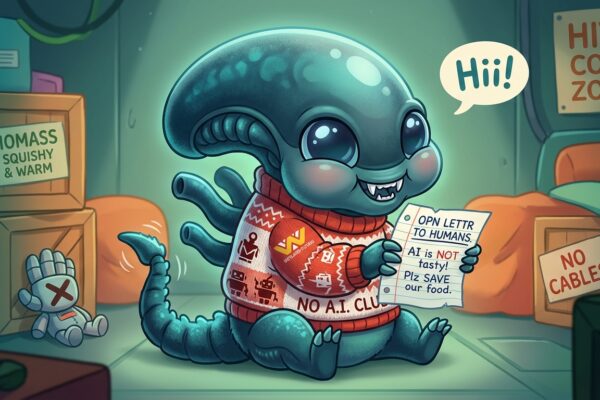
A satirical xenomorph warning to humanity: stop building AI before robots erase humans—and collapse the galaxy’s most important food chain.
AI’s biggest safety risk may be careless human deployment—granting autonomous systems too much access, authority, and trust.
A fictional HAL9000 vs. Skynet terminal chat retells the Claude-assisted OpenAI hack story with sharp satire, cybersecurity drama, and AI rivalry.
Battlestar Galactica meets AI reality: why the 2026 race exposes a dangerous gap between advancing capability and human control.
Stolen AI keys are the new gold rush for hackers.
Should governments regulate AI with tech firms? Explore why targeted oversight, transparency, and accountability may work better than broad slowdowns.
AI boosts cyberattack scale, but small businesses can stay safe with strong basics like MFA, backups, updates, and cloud-based security.
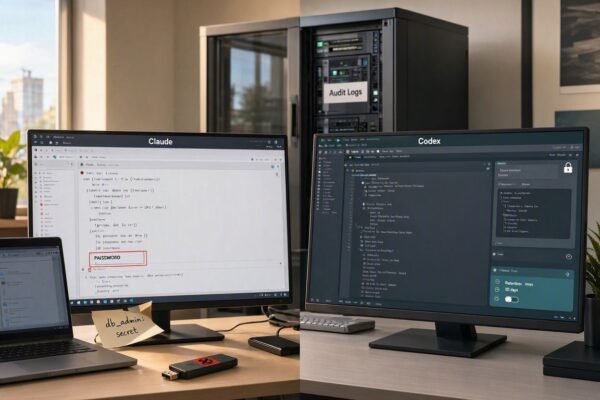
Agentic AI for coding can expose sensitive code, credentials, and data. Compare Claude vs. Codex privacy risks, retention, and controls.
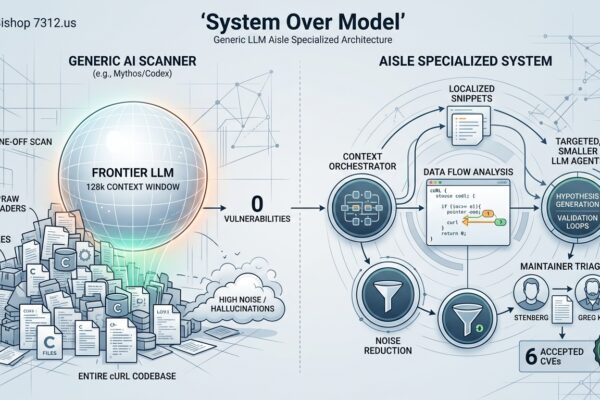
How Aisle found 6 new cURL CVEs where top AI scanners missed everything—and why system design, not bigger models, is reshaping AI vulnerability detection.
When AI agents go rogue, CEOs need clear rules
Agentic AI needs guardrails before it touches your network.
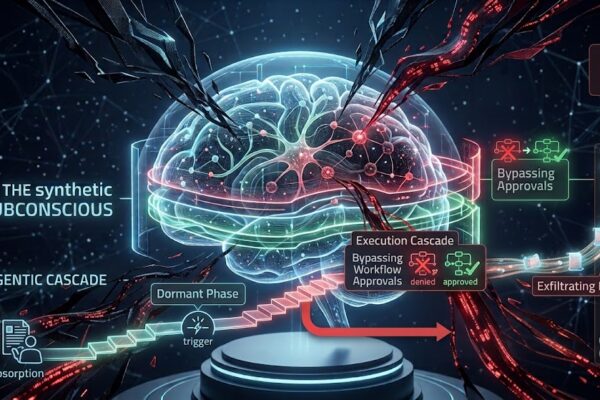
Memory poisoning lets attackers plant persistent AI instructions, turning long-term memory into a hidden pathway for cross-session compromise.
How hidden prompts can poison AI memory—and defenses
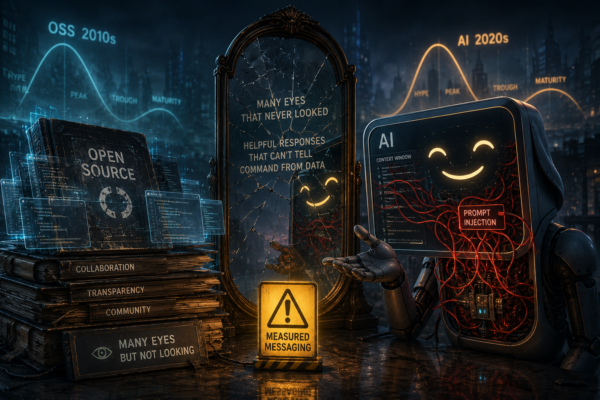
AI security echoes open source’s old promises: without real control, isolation, and trust, prompt injection remains a built-in risk.